
SMG
SyntheticMediaGuard
Examine images, video, audio, documents, browser media and live virtual meetings for signs the thing in front of you was made rather than captured.
Image & videoAudio & documentsLive meetings
Security and privacy are the two faces of the same coin
Detection for manipulated media, voice, identity and video runs beside consent, discovery, data requests and audit evidence
$ faceoff detect --stream video
> facial structure ... ok
> micro-expression .. ok
> ocular dynamics ... ok
cross-modal · 8 models
verdict: MANIPULATED$ faceoff consent --check crm
> notice version .... v4.2
> purpose scope ..... marketing
> downstream ack .... 11/11
append-only trail
verdict: WITHDRAWN$ faceoff verify --session onboard
> liveness .......... pass
> behaviour ......... anomalous
> approval path ..... flagged
identity · continuous
verdict: STEP UP$ faceoff cookies --scan domain
> cookies found ..... 214
> uncategorised ..... 18
> blocked pre-consent 9
policy-based control
verdict: UNCONSENTED$ faceoff voice --call inbound
> speaker verify .... fail
> acoustic profile .. synthetic
> call screening .... live
speaker intelligence
verdict: CLONED$ faceoff discover --scope estate
> stores scanned .... 428
> pii classified .... 61k
> unmapped copies ... 12
live catalogue
verdict: UNMAPPED$ faceoff credential --verify qr
> signature ......... valid
> post-quantum ...... ok
> identity graph .... 3 links
zero-trust chain
verdict: TAMPERED$ faceoff dpia --project onboard
> risks suggested ... 12
> mitigations ....... 9
> sign-off .......... pending
guided assessment
verdict: HIGH RISK$ faceoff osint --entity subject
> platforms ......... 27
> linked identities . 6
> corroboration ..... partial
investigation context
verdict: LINKED$ faceoff dsar --queue open
> identity verified . yes
> systems searched .. 34
> days remaining .... 6
statutory clock
verdict: DUE$ faceoff video --zone perimeter
> cameras ........... 42
> attribute match ... 1
> zone dwell ........ 03:14
movement intelligence
verdict: INTRUSION$ faceoff audit --scope programme
> controls mapped ... 118
> evidence items .... 2,410
> gaps detected ..... 4
evidence timeline
verdict: GAPS FOUND$ faceoff slm --deploy on-prem
> egress ............ none
> prompts retained .. local
> governance ........ enforced
inside your perimeter
verdict: CONTAINED$ faceoff ask --scope dpdp
> sources cited ..... 7
> controls matched .. 18
> draft response .... ready
grounded in your evidence
verdict: ANSWERED$ faceoff detect --stream video
> facial structure ... ok
> micro-expression .. ok
> ocular dynamics ... ok
cross-modal · 8 models
verdict: MANIPULATED$ faceoff consent --check crm
> notice version .... v4.2
> purpose scope ..... marketing
> downstream ack .... 11/11
append-only trail
verdict: WITHDRAWN$ faceoff verify --session onboard
> liveness .......... pass
> behaviour ......... anomalous
> approval path ..... flagged
identity · continuous
verdict: STEP UP$ faceoff cookies --scan domain
> cookies found ..... 214
> uncategorised ..... 18
> blocked pre-consent 9
policy-based control
verdict: UNCONSENTED$ faceoff voice --call inbound
> speaker verify .... fail
> acoustic profile .. synthetic
> call screening .... live
speaker intelligence
verdict: CLONED$ faceoff discover --scope estate
> stores scanned .... 428
> pii classified .... 61k
> unmapped copies ... 12
live catalogue
verdict: UNMAPPED$ faceoff credential --verify qr
> signature ......... valid
> post-quantum ...... ok
> identity graph .... 3 links
zero-trust chain
verdict: TAMPERED$ faceoff dpia --project onboard
> risks suggested ... 12
> mitigations ....... 9
> sign-off .......... pending
guided assessment
verdict: HIGH RISK$ faceoff osint --entity subject
> platforms ......... 27
> linked identities . 6
> corroboration ..... partial
investigation context
verdict: LINKED$ faceoff dsar --queue open
> identity verified . yes
> systems searched .. 34
> days remaining .... 6
statutory clock
verdict: DUE$ faceoff video --zone perimeter
> cameras ........... 42
> attribute match ... 1
> zone dwell ........ 03:14
movement intelligence
verdict: INTRUSION$ faceoff audit --scope programme
> controls mapped ... 118
> evidence items .... 2,410
> gaps detected ..... 4
evidence timeline
verdict: GAPS FOUND$ faceoff slm --deploy on-prem
> egress ............ none
> prompts retained .. local
> governance ........ enforced
inside your perimeter
verdict: CONTAINED$ faceoff ask --scope dpdp
> sources cited ..... 7
> controls matched .. 18
> draft response .... ready
grounded in your evidence
verdict: ANSWERED
Bring privacy and security inside your perimeter. It brings data discovery, consent and protection along with security intelligence in an on-premise appliance, keeping sensitive processing within your infrastructure
Deploy inside your infrastructure, with options for isolated environments
Discover sensitive data, manage consent and protect what you share
Connect identity, voice and media signals to investigate threats
Keep control activity and supporting evidence ready for review
One operating layer: security teams connect signals into explainable evidence, while privacy teams manage consent, data requests and their compliance record
Fifteen engines in, one verdict out, with the working behind it
The multimodal intelligence engine behind every FaceOff verdict
Three pillars. One platform: Security Intelligence, Privacy, and Governance
Manipulated media, identity fraud, suspicious voices, digital threats and physical-world risk, read through one connected intelligence layer that can stay inside your perimeter.
Explore security intelligenceOne surface for consent, cookies, discovery, assessments, DSARs and audit evidence, with an AI copilot reading 1,200+ regulations against your own controls.
Explore privacy operationsModel inventory, lineage and the algorithmic due diligence Sec. 10 now requires, assessed against nine regimes from one description of the system.
Inside AI GovernanceExamine images, video, audio, documents, browser media and live virtual meetings for signs the thing in front of you was made rather than captured.
Assess the person behind an interaction through liveness checks and behavioural patterns, so an approval carries evidence of who gave it.
Combine speaker verification, acoustic profiling and real-time call screening to investigate a voice and the call it arrived on.
Verify credentials and their packaging with post-quantum signatures, secure QR and identity-graph analysis.
Analyse public information, digital footprints and the connections between identities across platforms to give an investigation its context.
Search camera footage by attribute, follow movement across cameras, and watch protected zones for perimeter defence.
Run an in-house small language model on your own infrastructure, so prompts and findings stay inside your perimeter.
The whole security suite on one on-premise appliance: media, voice, identity and threat engines inside your perimeter, with nothing sent out for scoring.
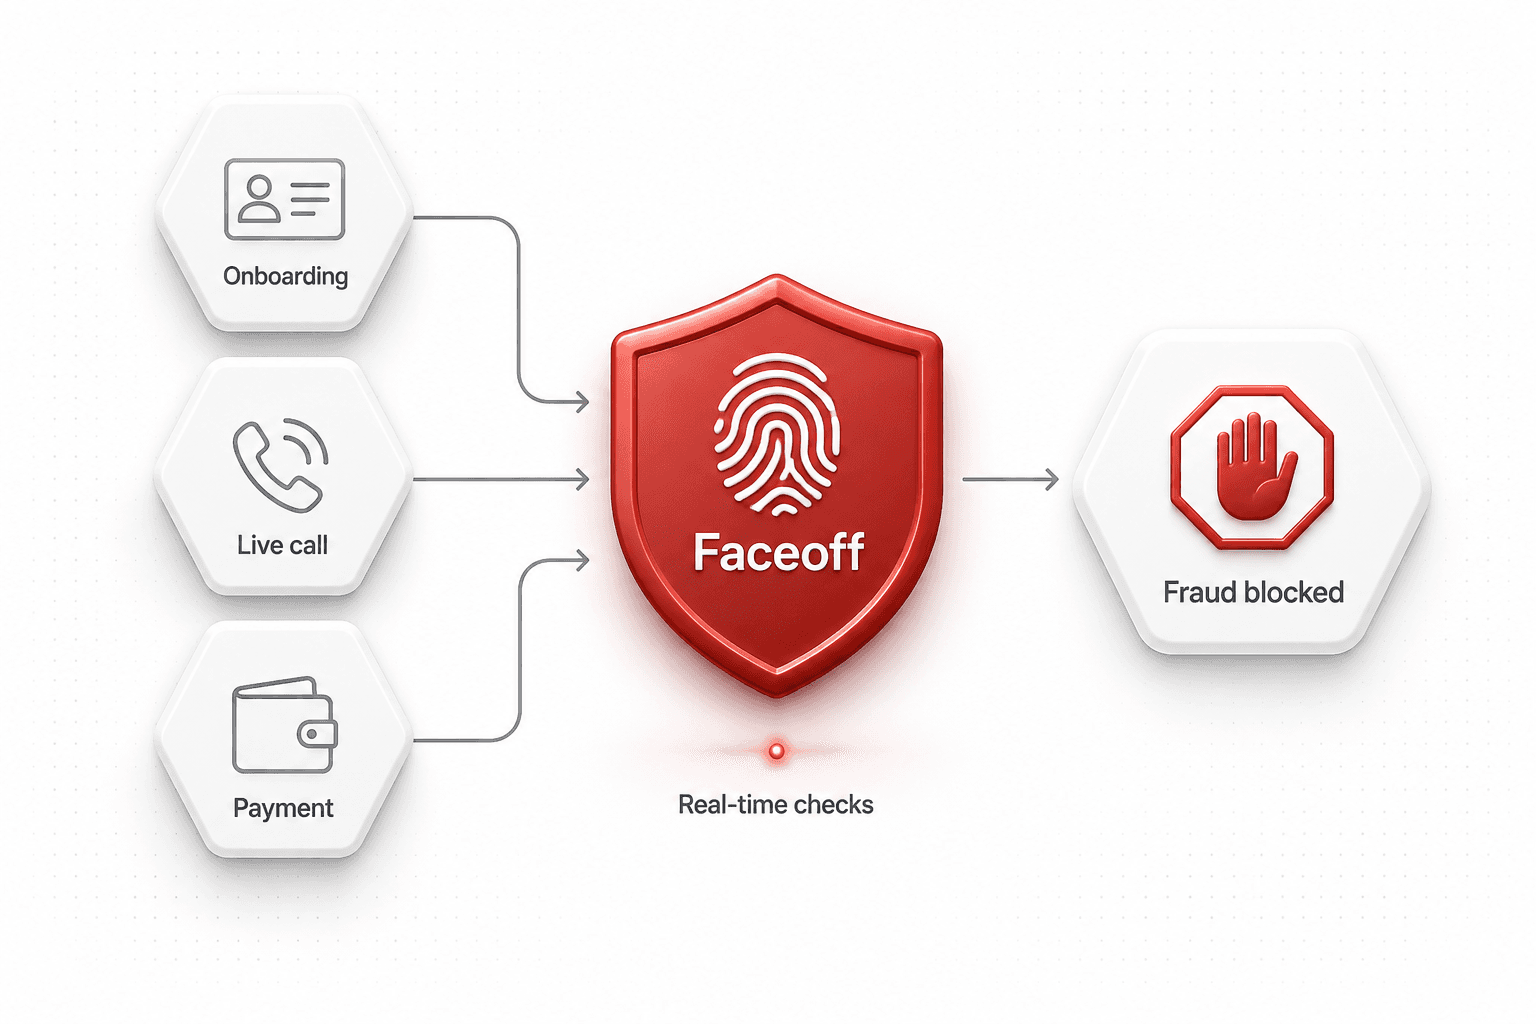
Impersonation is caught at onboarding, in the call and at the payment, while the transaction can still be refused, not in the reconciliation that follows it
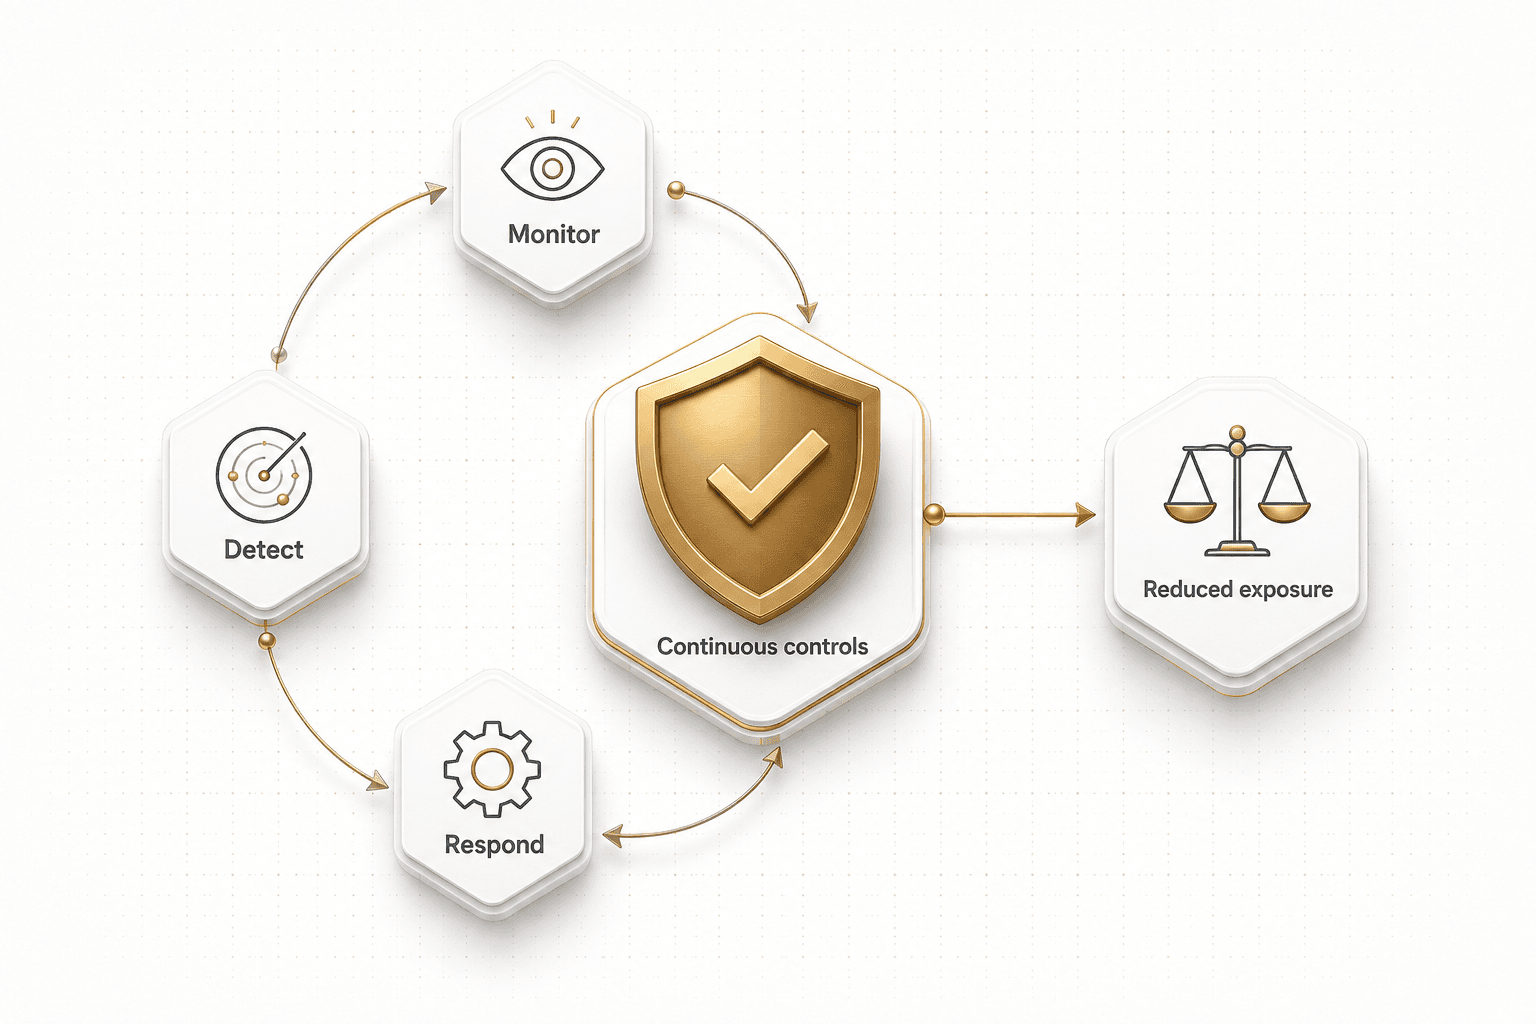
The DPDP Act carries up to ₹250 Cr for a failure of reasonable security safeguards, assessed per instance. Controls that run continuously are what stands between you and that number
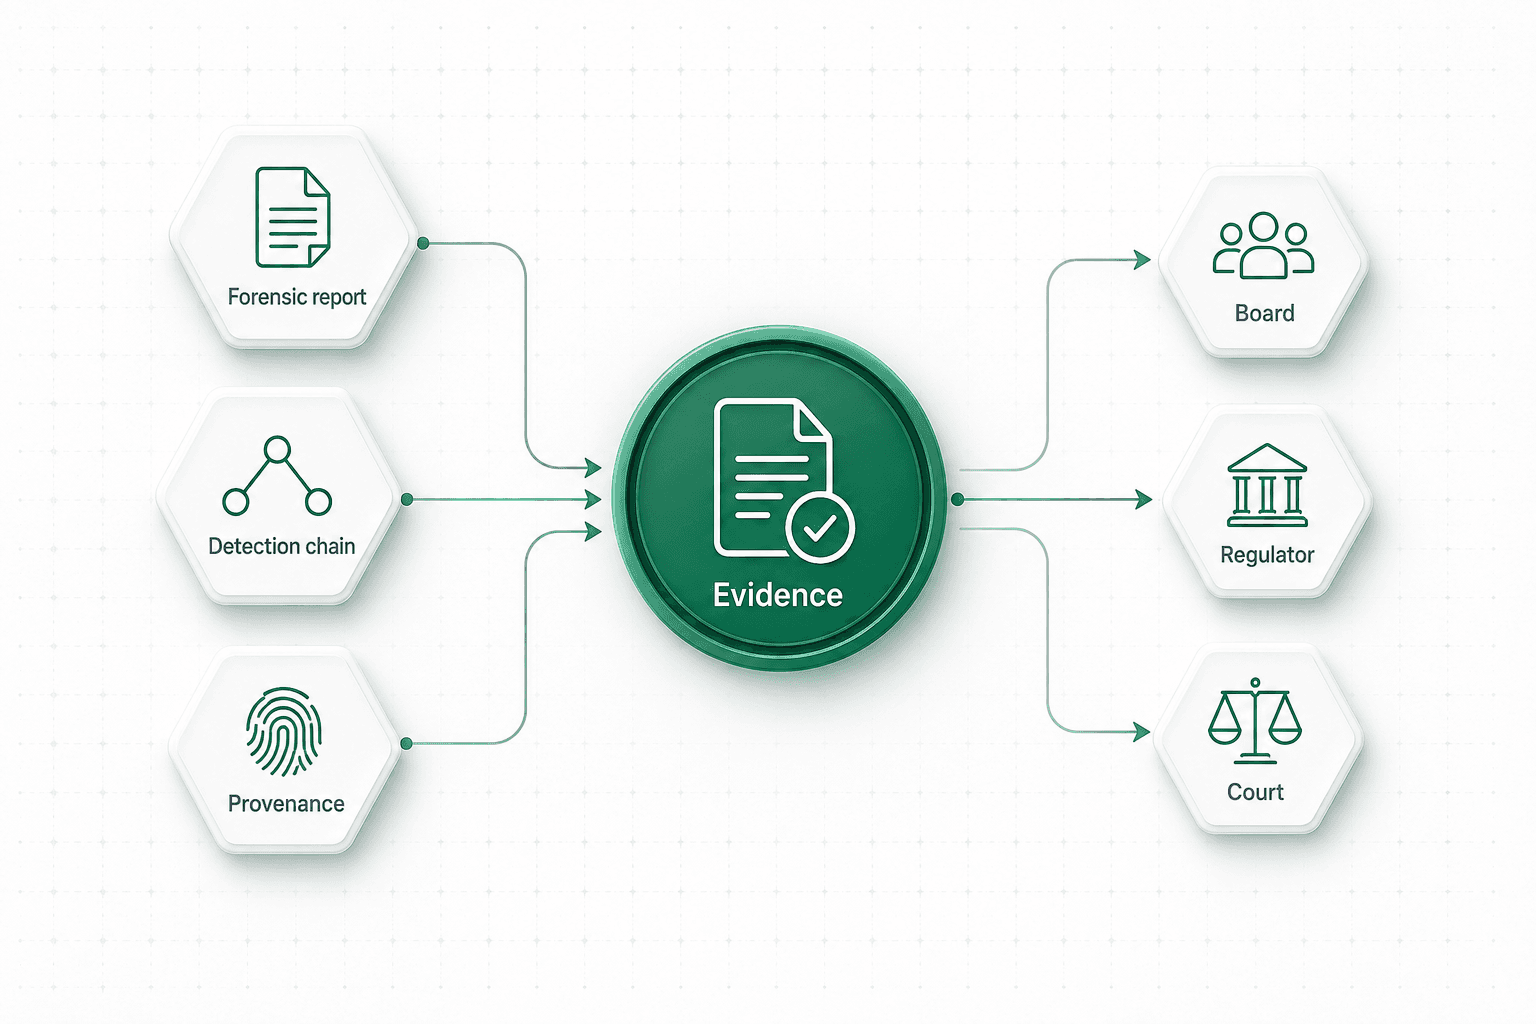
Forensic reports, per-decision detection chains and provenance tiers on every output mean a finding can be defended to a board, a regulator or a court
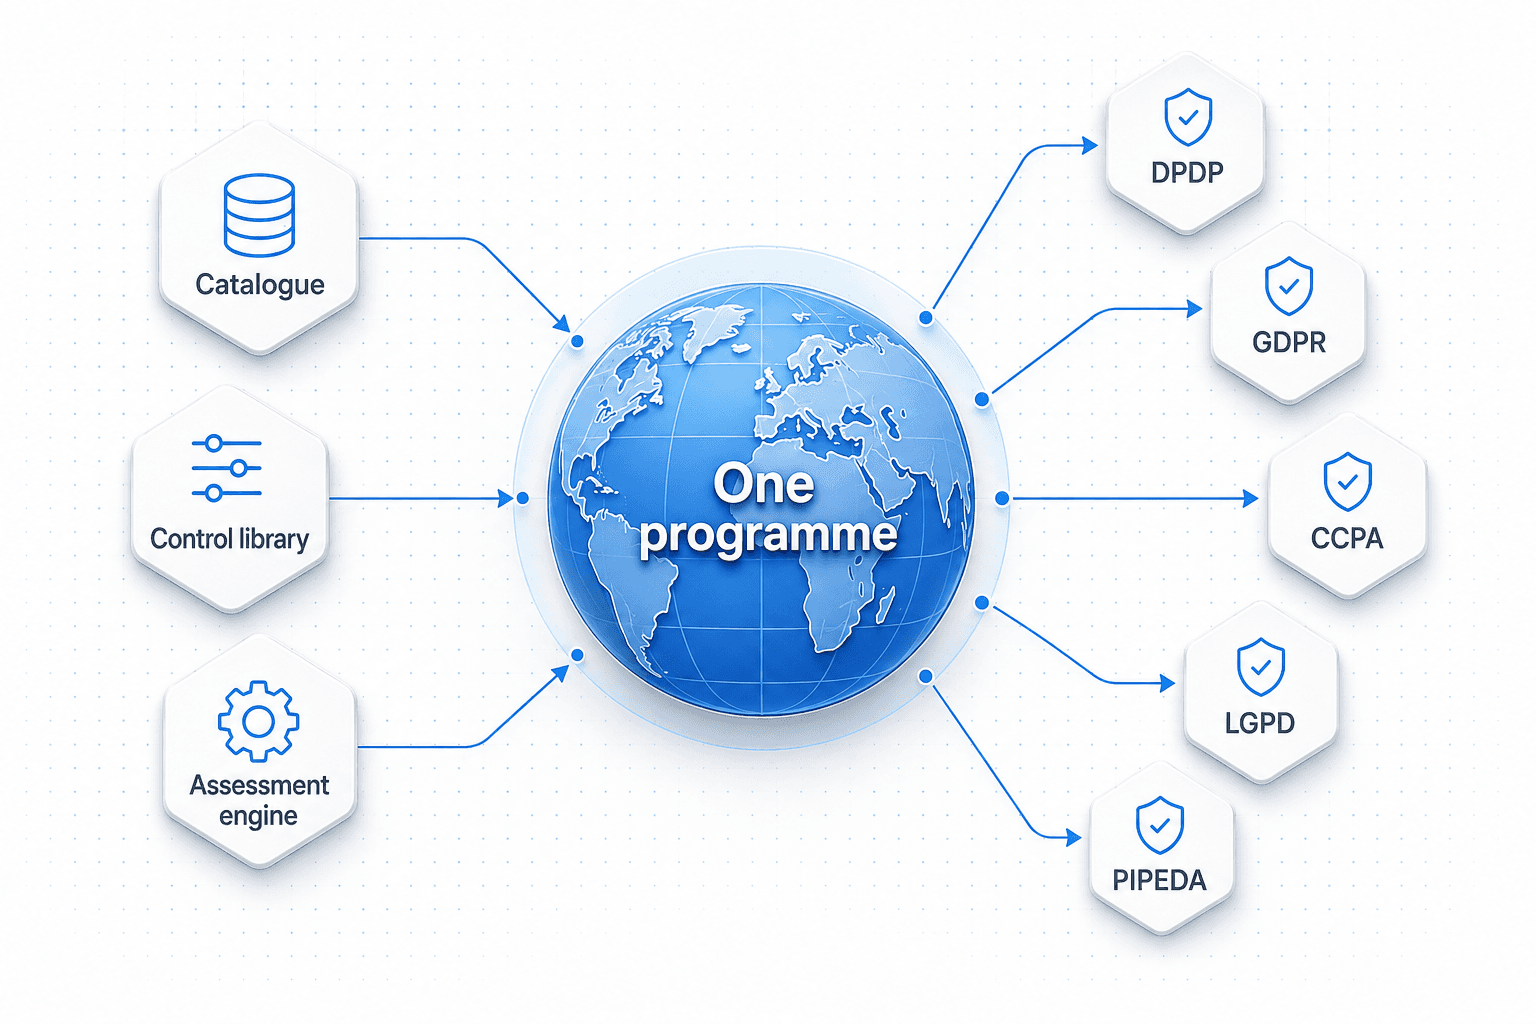
One catalogue, one control library and one assessment engine serve every regime you are in scope for, instead of a separate project each time a jurisdiction moves
It detects deepfakes, manipulated media, synthetic voices, identity fraud and digital threats across image, video, audio and documents, then connects those signals into one investigation so teams see the whole picture instead of one alert
Consent, cookies, data discovery, PIA and DPIA assessments, DSARs and audit evidence run from one privacy graph, so every record, control and request shares a single source of truth across your organisation
An AI copilot reads more than 1,200 regulations including India DPDP, GDPR, CCPA and the EU AI Act against your own controls and evidence, and answers with citations so compliance teams always know the practical next step
Every security verdict keeps its supporting observations and every privacy action keeps its evidence timeline in an append only record, so a regulator, a board or an investigator can see exactly how a decision was reached
Yes, deploy as managed cloud, private cloud, on premise, edge or fully air gapped, including the in a Box appliance, so sensitive media, personal data and prompts never have to leave your perimeter
One engine, the Trust Factor, scores media, identity, voice, consent and data risk together, which removes duplicate tooling, closes the gaps between teams and gives leadership one trusted answer instead of five dashboards

Investigate what is real, know where personal data lives, and keep the evidence to explain both, before a regulator, a board or an attacker asks you to