Software Due Diligence & M&A Technology Audits
Examine public code contributions, developer activity, and external dependency health of acquisition targets and commercial technology partners.
How the sector deploys itDiscover, analyse and assess publicly accessible GitHub repositories and open-source development activity: search public code, evaluate project metadata and commit histories, identify software dependencies and public technical signals, and support authorised security reviews while ensuring sensitive findings are handled responsibly.
Where it looks
Interface simulation: an illustration of the workflow, not a live analysis
What it is
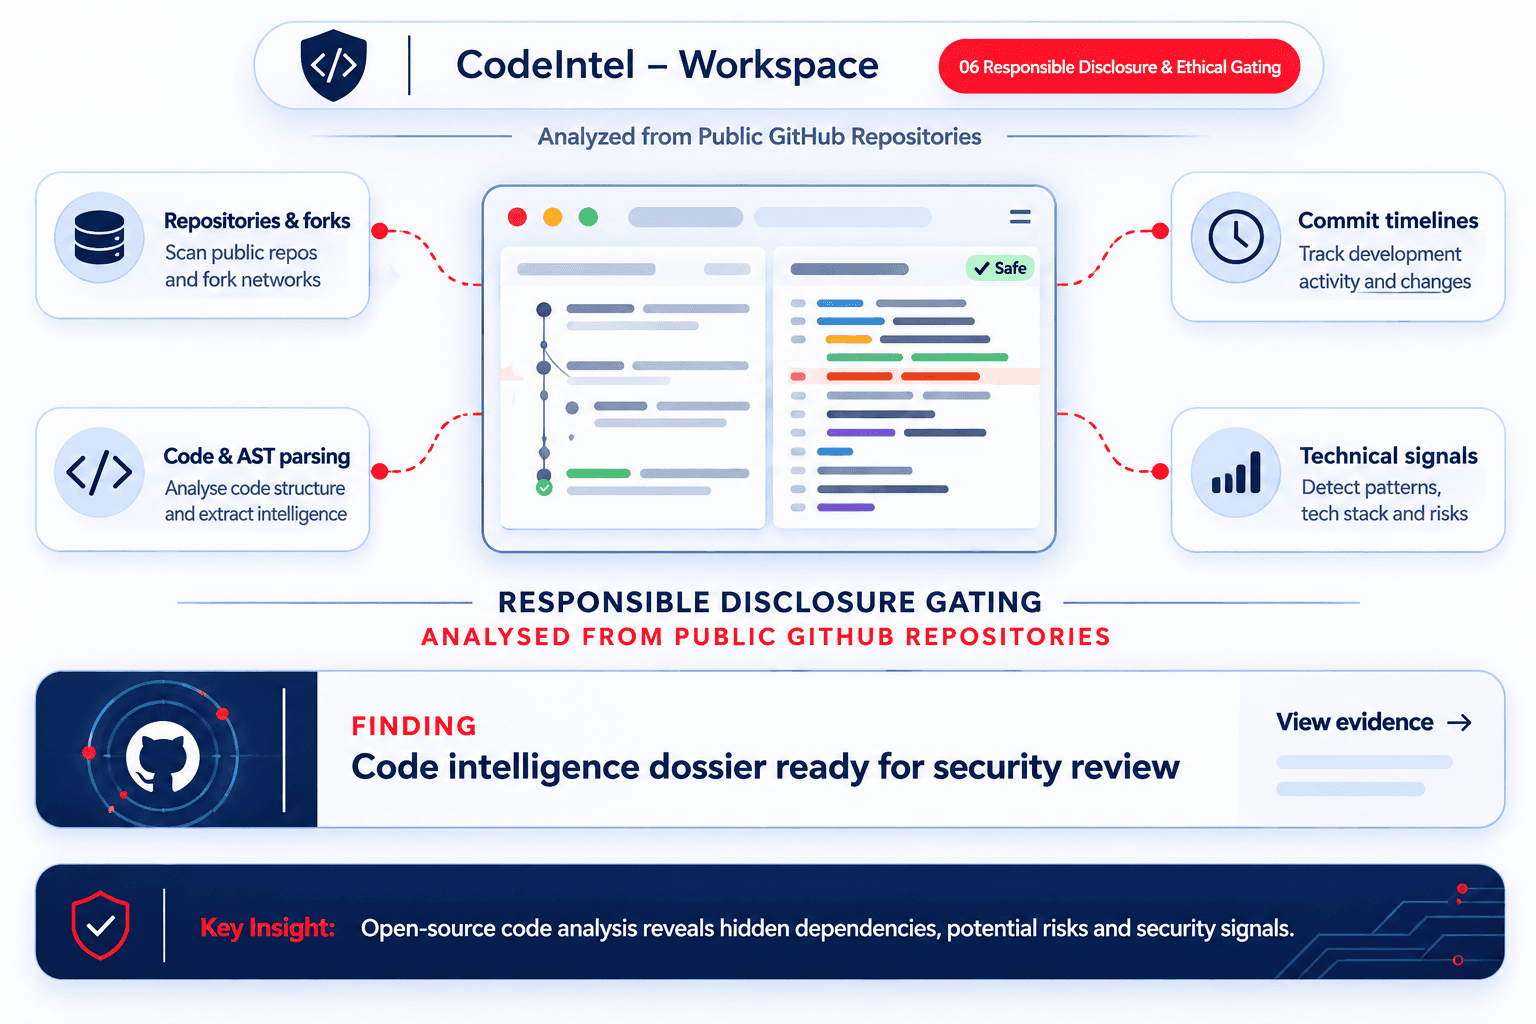
CodeIntel is a code intelligence solution focused on publicly accessible GitHub repositories and open-source development activity. It helps researchers and security teams discover relevant repositories, examine code and project metadata, and identify useful technical information across public development resources.
This can support software research, technology assessment, open-source due diligence and authorised security reviews, while helping teams understand project activity and relationships between repositories. CodeIntel’s value is in making large volumes of public code information easier to search and assess, so analysts can focus on relevant findings rather than manual repository browsing.
Typical capabilities include repository discovery, code and metadata analysis, and review of public development signals; any identified secrets, vulnerabilities or sensitive data should be handled responsibly and disclosed through appropriate channels.
Key capabilities include search and discovery of public repositories, analysis of publicly available code and metadata, and review of project and development activity.
Public repositories
Discovers and indexes publicly accessible GitHub repositories, branches and fork trees
Code & metadata
Examines source syntax, dependency manifests, commit signatures and contributor trails
Development signals
Analyzes release cadence, contributor velocity, issue lifecycles and repository relationships
Responsible review
Equips analysts with responsible disclosure boundaries; sensitive secrets handled through ethical workflows
Interactive Code Discovery
Explore public repository trees, AST syntax extraction, commit provenance timelines, and open-source signals.
Semantic code discovery, AST syntax tree analysis, commit provenance and dependency mapping.
cloud-telemetry/cyber-mesh-gateway
High-throughput asynchronous zero-trust service proxy and distributed telemetry mesh controller.
lead-sec-eng (@marcus-mesh)
Commit 7b4e91a · 3 days ago
func (v *JWTValidator) VerifyBearerToken(tokenStr string) (*Claims, error) {
    parsed, err := jwt.ParseWithClaims(tokenStr, &Claims{}, v.KeyFunc)
    if err != nil || !parsed.Valid {
        return nil, ErrInvalidSignature
    }
    return parsed.Claims.(*Claims), nil
}Implements strict cryptographic signature validation using public JWKS endpoint. Public source code reveals no hardcoded secrets or permissive bypass routines.
Lawful public repository analysis. Code syntax parsing verifies absence of insecure algorithmic downgrade attacks.
How it works
Specify target organisations, keywords, author handles, or code signatures in scope
Query open GitHub APIs, traverse repository networks, and map upstream fork lineage
Inspect file trees, language distributions, license types, and dependency manifests
Extract commit author identities, PGP signatures, timestamp drifts, and change diffs
Surface package manifests, external API endpoints, container configs, and shared modules
Flag potential sensitive exposures with ethical handling boundaries and secure reporting channels
Synthesise normalised repository inventories, risk findings, and audit-compliant case reports
Interface simulation: an illustration of the workflow, not a live analysis
Specify target organisations, keywords, author handles, or code signatures in scope
Query open GitHub APIs, traverse repository networks, and map upstream fork lineage
Inspect file trees, language distributions, license types, and dependency manifests
Extract commit author identities, PGP signatures, timestamp drifts, and change diffs
Surface package manifests, external API endpoints, container configs, and shared modules
Flag potential sensitive exposures with ethical handling boundaries and secure reporting channels
Synthesise normalised repository inventories, risk findings, and audit-compliant case reports
Capabilities
Replace tedious manual web browsing with systematic, multi-repository analysis and dependency tracking.
Public repository discovery & fork lineage
Interface simulation: an illustration of the workflow, not a live analysis
Comparison
Why structured repository intelligence beats manual web browsing and ad-hoc scraping scripts.
Multi-repository discovery & fork tracking
Deep commit history & author provenance
Dependency manifest & architecture mapping
Responsible disclosure & sensitive data guardrails
Public-only non-invasive OSINT compliance
Sovereign private deployment & query secrecy
Structured audit trail & JSON / CSV export
The architecture
AST syntax extraction, commit history provenance, and sovereign technical signal analysis
Identifies target public repositories, developer handles, software dependencies, or technical keywords in scope
Normalizes public repository trees, parses AST patterns, and establishes commit timeline provenance
Strictly lawful OSINT from publicly accessible GitHub repositories and open-source resources. Repository queries, syntax trees, and analysis dossiers remain entirely within your sovereign environment. Any identified secrets or vulnerabilities must be handled responsibly and disclosed through appropriate channels.
Navigable code tree, commit timeline visualizer, and public repository topology graph
Audit-ready technical reports with contributor provenance, repository metadata, and security findings
Measured capabilities
100M+ Public commits
Capable of querying deep historical commit logs, diff histories, and branch archives across public repositories
100% Public data
Operates strictly on open repositories without private credential theft, token bypass or API abuse
Seconds per repository
Replaces days of tedious manual file-by-file inspection with instant AST and dependency parsing
Zero query leakage
Target search terms, repository lists, and vulnerability dossiers remain inside your sovereign boundary
CodeIntel is built for authorized security assessments, open-source due diligence and software research; identified exposures must be handled in accordance with responsible disclosure principles.
Sectors
Examine public code contributions, developer activity, and external dependency health of acquisition targets and commercial technology partners.
How the sector deploys itDiscover unmaintained dependencies, exposed configuration files, and public fork sprawl to maintain external software supply chain visibility.
How the sector deploys itTrack suspicious repository releases, typosquatted package names, and coordinated code commit patterns linked to adversary operations.
How the sector deploys itIdentify unauthorized public repositories duplicating proprietary code, brand assets, or sensitive project templates across public accounts.
How the sector deploys itDeployment
Designed for immediate deployment with zero exposure of sensitive investigation keywords.
01 · Define repository scope and compliance parameters
Interface simulation: an illustration of the workflow, not a live analysis
The principle
Moving from manual repository browsing to structured, automated and defensible open-source intelligence.
CodeIntel is FaceOff's code intelligence solution within TrustShield OSINT. It focuses on publicly accessible GitHub repositories and open-source development activity to help teams discover repositories, analyse code metadata, and assess technical projects.
No. CodeIntel operates strictly on publicly accessible repositories, open-source code, and public development activity. It does not access private repositories or bypass GitHub access controls.
CodeIntel is designed for responsible security review. Any identified sensitive information (such as accidentally committed API keys or credentials) must be handled responsibly and reported through established disclosure channels rather than exploited.
Yes. CodeIntel parses package manifests across major package ecosystems (npm, PyPI, Go, Maven, Cargo) to catalog third-party dependencies, license distributions, and external library references.
When installed on premises or within your private cloud, all target keywords, repository clones, and investigation dossiers remain strictly within your sovereign environment. Nothing is sent to external data brokers.
CodeIntel exports structured findings in JSON, CSV, and PDF dossier formats, including repository URLs, commit hashes, dependency inventories, and timestamped audit logs for compliance.
The rest of the line
See how CodeIntel helps software researchers, due diligence reviewers and security teams replace manual repository browsing with structured code intelligence.