Law enforcement and cybercrime
Investigate handles observed in illicit forums, cyber incident reports or fraud schemes, uncovering public social and developer footprints across the open web.
How the sector deploys itIdentify publicly accessible accounts associated with a known username across online platforms and services: reveal linked profiles, eliminate repetitive manual searching, and structure leads for authorised investigations while preserving ethical safeguards.
Where it looks
Interface simulation: an illustration of the workflow, not a live analysis
What it is
UserIntel is a username intelligence solution designed to help investigators, security teams and researchers identify publicly accessible accounts associated with a known username across online platforms and services. By checking username presence across multiple sources and consolidating relevant public results, UserIntel can help reveal linked profiles, support digital identity research and provide useful leads for authorised investigations.
Its value lies in reducing the time spent on repetitive manual searches while giving analysts a more structured view of a username's observable online presence. Typical capabilities include cross-platform username searches, profile discovery, result organisation and investigation-ready reporting.
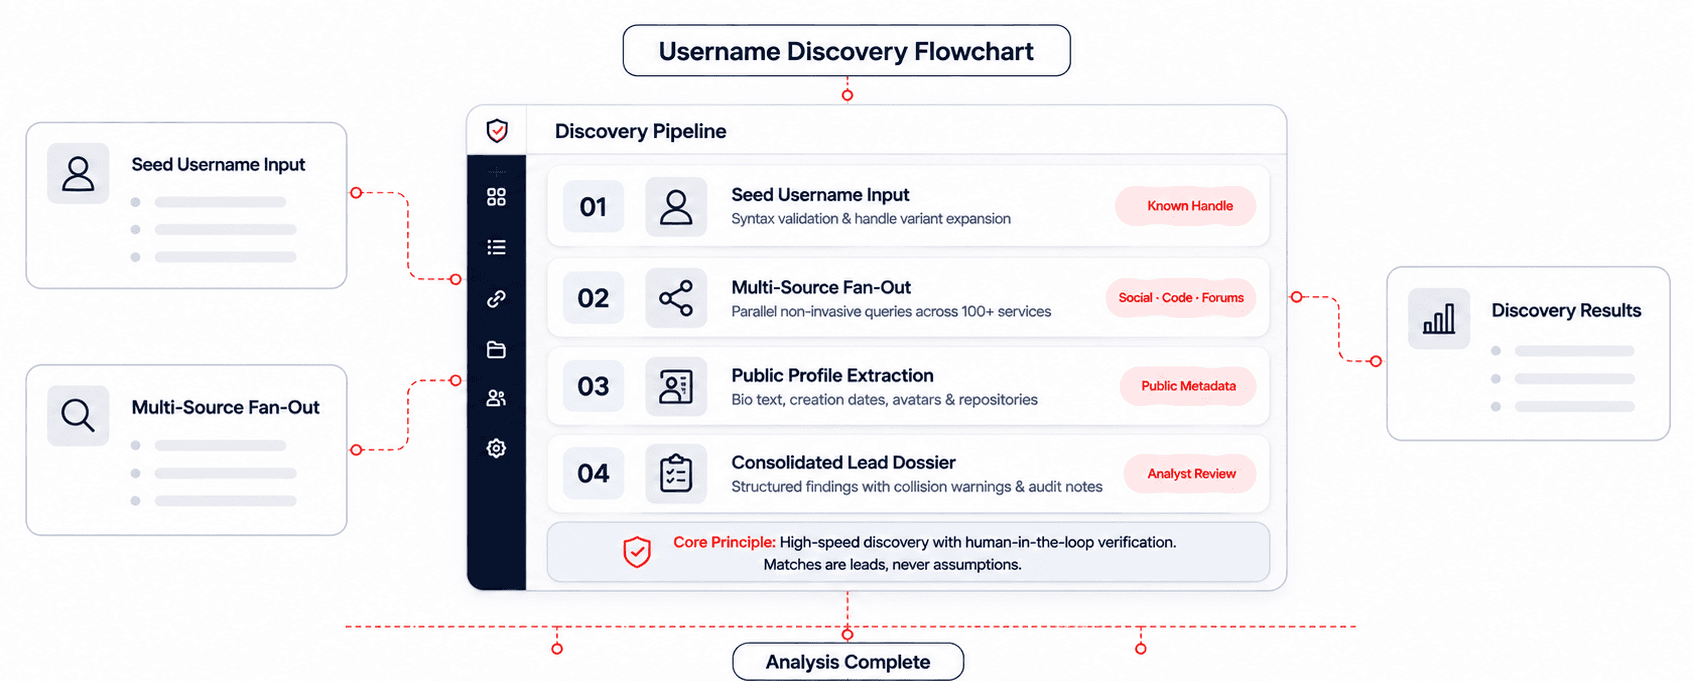
Rather than switching between dozens of browser tabs and manually testing profile URLs, an analyst enters a target username once. UserIntel performs non-invasive presence queries across more than one hundred services, harvests publicly observable profile metadata, and brings the findings into one organized review workspace.
UserIntel is intended for lawful, ethical use of publicly available information; a matching username should be treated as a lead rather than proof that accounts belong to the same person.
100+ Platforms
Check username availability and public profiles across social networks, code repositories, forums and registries
Observable only
Operates exclusively on publicly accessible sources without accessing private or gated data
Lead generation
Matches are surfaced as investigative leads with reasons shown, rather than proof of identity
Analyst controlled
Search results, correlation notes and case records stay within infrastructure your organisation controls
How it works
Syntax validation, character sets & handle variants
Non-invasive checks across 100+ online platforms
Examine HTTP response codes, headers & existence
Harvest publicly visible bios, join dates & metadata
Identify common aliases, bio overlap & handle collisions
Organise observable profiles by relevance and signal strength
Case-ready report with full source attribution
Interface simulation: an illustration of the workflow, not a live analysis
Syntax validation, character sets & handle variants
Non-invasive checks across 100+ online platforms
Examine HTTP response codes, headers & existence
Harvest publicly visible bios, join dates & metadata
Identify common aliases, bio overlap & handle collisions
Organise observable profiles by relevance and signal strength
Case-ready report with full source attribution
What sets it apart
Cross-platform username searches at scale
Interface simulation: an illustration of the workflow, not a live analysis
How it compares
Manual searching is slow and prone to missed platforms, while unguided scrapers generate excessive false positives. UserIntel provides structured, ethical username intelligence designed for analysts.
100+ platform simultaneous query
Public profile & metadata extraction
Username collision guarding
Time to complete comprehensive search
Strict adherence to public information only
Confidential deployment & query privacy
Structured investigation-ready dossier
The architecture
Cross-platform presence queries, response verification, and structured analyst lead generation
Syntax normalisation · handle variant synthesis
Username Discovery & Verification Core
Non-invasive HTTP queries across 100+ platforms with collision detection
Queries run without accessing private credentials or gated accounts. All data processed within organisational infrastructure.
Observable accounts grouped with confidence metrics
Traceable evidence records with analyst audit notes
Lawful & Ethical OSINT Posture: Matching usernames represent investigative leads for human analysts to examine, not conclusive proof of common individual ownership.
Evidence and trust
Public provenance
Every discovered account links directly to its publicly accessible profile URL
Timestamped trail
Exact time and date of discovery preserved for legal and evidentiary integrity
Analyst oversight
Matches are flagged as investigative leads requiring human corroboration
Zero invasive access
No passwords, tokens or privacy bypasses used in the discovery process
Because public usernames are non-exclusive across independent services, UserIntel couples automated discovery with transparent correlation indicators, ensuring investigations stay grounded in verified evidence rather than hasty assumptions.
Use cases by sector
Investigate handles observed in illicit forums, cyber incident reports or fraud schemes, uncovering public social and developer footprints across the open web.
How the sector deploys itTrack adversary aliases, examine public GitHub repositories associated with malware author handles, and uncover threat actor footprints across public infrastructure.
Identify accounts impersonating corporate leaders, brand names or official domain handles across social media and messaging platforms before fraud occurs.
How the sector deploys itDiscover accounts using the same username across online marketplaces, forums and platforms to identify repeat fraudsters and multi-account scams.
Support digital identity research and open-source intelligence workflows with fast discovery, structured profiles and responsible lead classification.
Verify public disclosures of counterparties or key personnel and map observable digital presence to support comprehensive background evaluations.
How the sector deploys itDeployment strategy
01 · Define operational scope
Interface simulation: an illustration of the workflow, not a live analysis
Whether searching a single handle during an urgent incident or running background research on an extended dossier, UserIntel applies the same rigorous verification and ethical lead framing to every result.
What it has to get right
Four commitments of responsible username intelligence.
UserIntel is a username intelligence solution designed to help investigators, security teams and researchers identify publicly accessible accounts associated with a known username across online platforms and services.
UserIntel performs non-invasive checks against publicly visible account endpoints and open profile URLs across more than 100 online platforms. It validates existence through response status codes, extracts observable public metadata, and aggregates the results for analyst review.
No. A matching username should be treated as an investigative lead rather than proof that accounts belong to the same person. Common usernames frequently collide across different services. UserIntel provides correlation indicators (e.g. matching avatar, bio keywords, timezone) to assist analysts in deciding whether accounts are related.
No. UserIntel operates exclusively on information that is publicly accessible to any web browser. It does not bypass privacy walls, crack passwords, or exploit unauthorised APIs.
UserIntel queries social networks, open-source code repositories (GitHub, GitLab), community forums (Reddit, HackerNews), messaging registries (Telegram), blogging sites, and public directory services.
Manually checking dozens of websites for a single username takes hours of repetitive typing and verification. UserIntel checks 100+ platforms in seconds, eliminating manual errors and delivering a structured summary directly to the analyst.
No. When deployed in your organisation's controlled environment, queries originate from your infrastructure and results are stored locally. UserIntel does not send target identifiers to external data brokers.
UserIntel exports structured investigation-ready dossiers including timestamped lists of discovered profiles, source URLs, extracted bios, metadata tags, and analyst notes in PDF, JSON, and CSV formats.
Yes, when conducted lawfully for legitimate purposes using publicly accessible information. UserIntel is built for lawful, ethical investigations adhering to data protection standards and platform acceptable use guidelines.
Yes. UserIntel provides REST APIs and structured data outputs that integrate into intelligence platforms, SIEM/SOAR pipelines, and case management suites.
The rest of the line
Where it runs
Each sector page covers the threat model, the controls, and the regulators that apply.
See how UserIntel helps investigators discover public accounts across 100+ platforms in seconds, with structured reporting and built-in ethical safeguards.